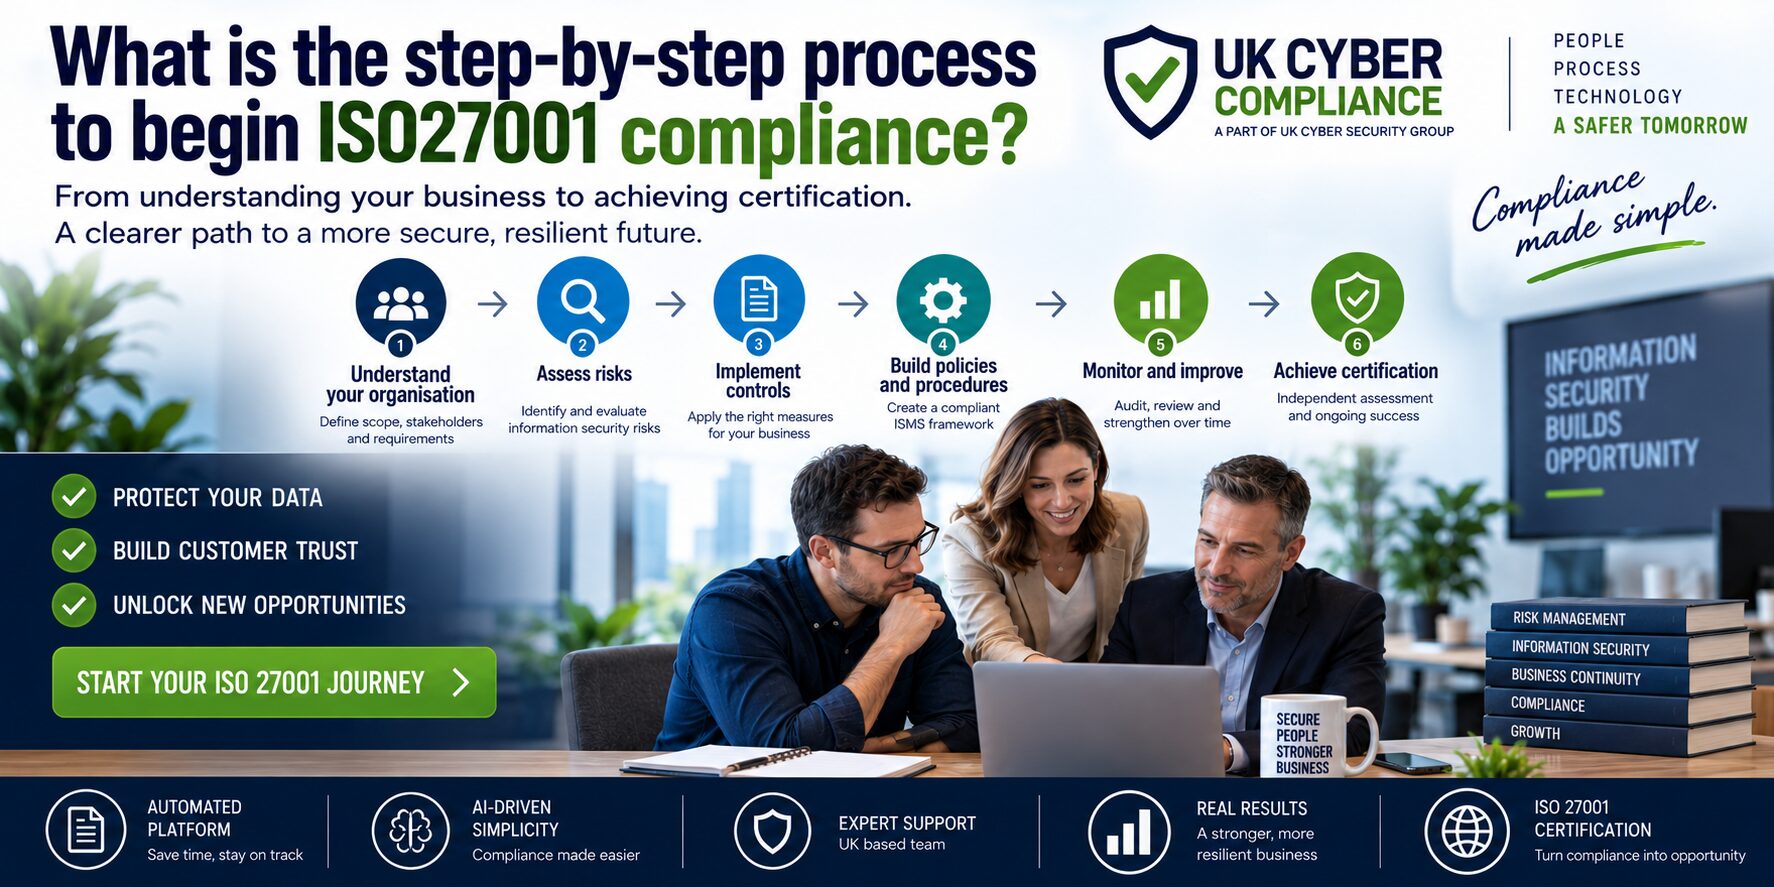
The step-by-step process to begin ISO27001 compliance starts with understanding your organisation rather than immediately writing policies or working through security controls.
Cybersecurity News and Compliance Insights
Stay informed with the latest cyber threats, regulatory updates, and expert guidance to help your business stay secure and compliant.
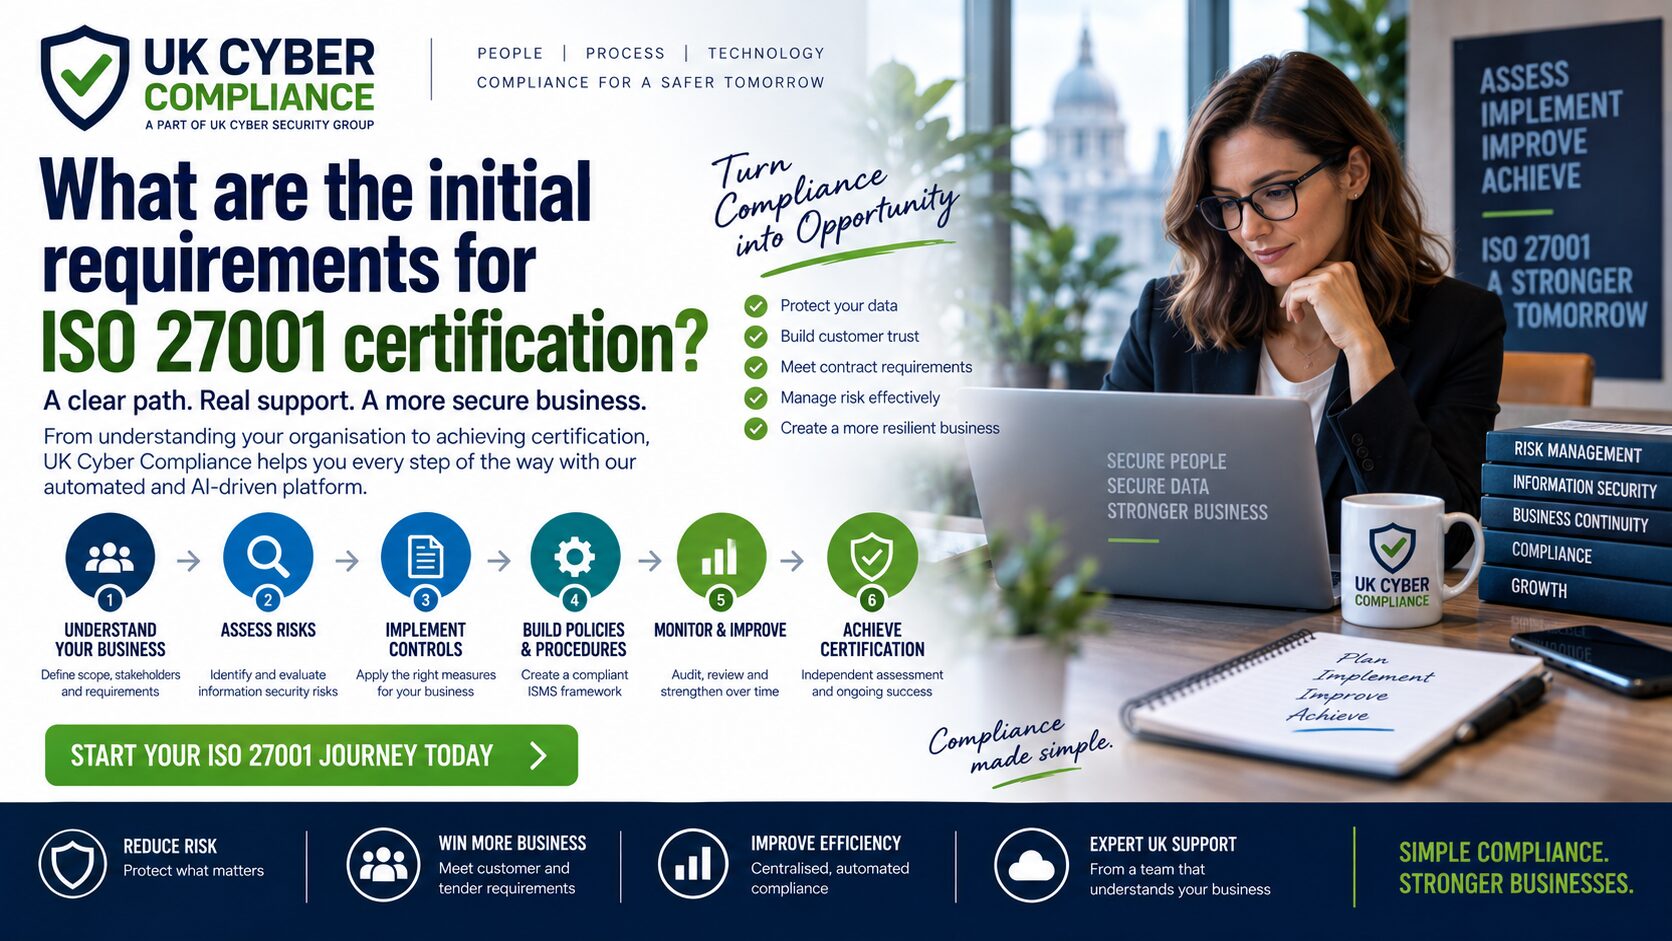
What are the initial requirements for ISO 27001 certification?
The initial requirements for ISO 27001 certification start long before an external auditor arrives. A business first needs to understand why it wants certification, what part of the organisation the Information Security Management System will cover, who will take responsibility for it, what information needs protection and which security risks matter most.
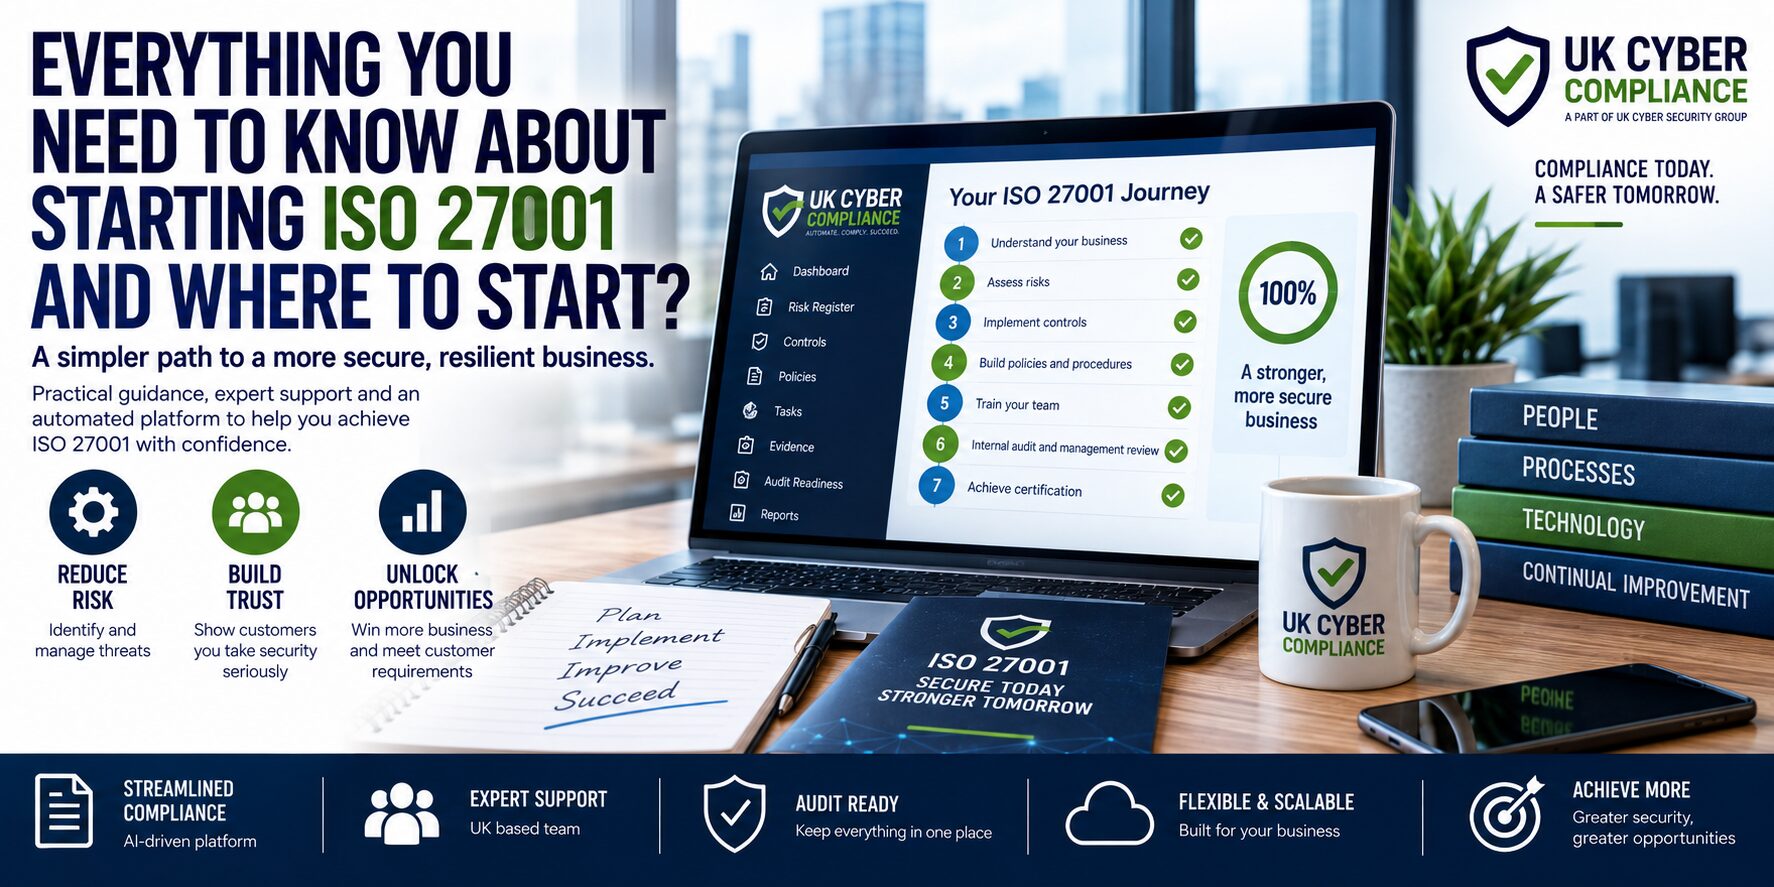
Everything you need to know about starting ISO 27001 and where to start?
Starting ISO 27001 can look complicated when you first see the standard. There are risks to assess, controls to consider, policies to prepare, responsibilities to assign, audits to complete and evidence to gather.
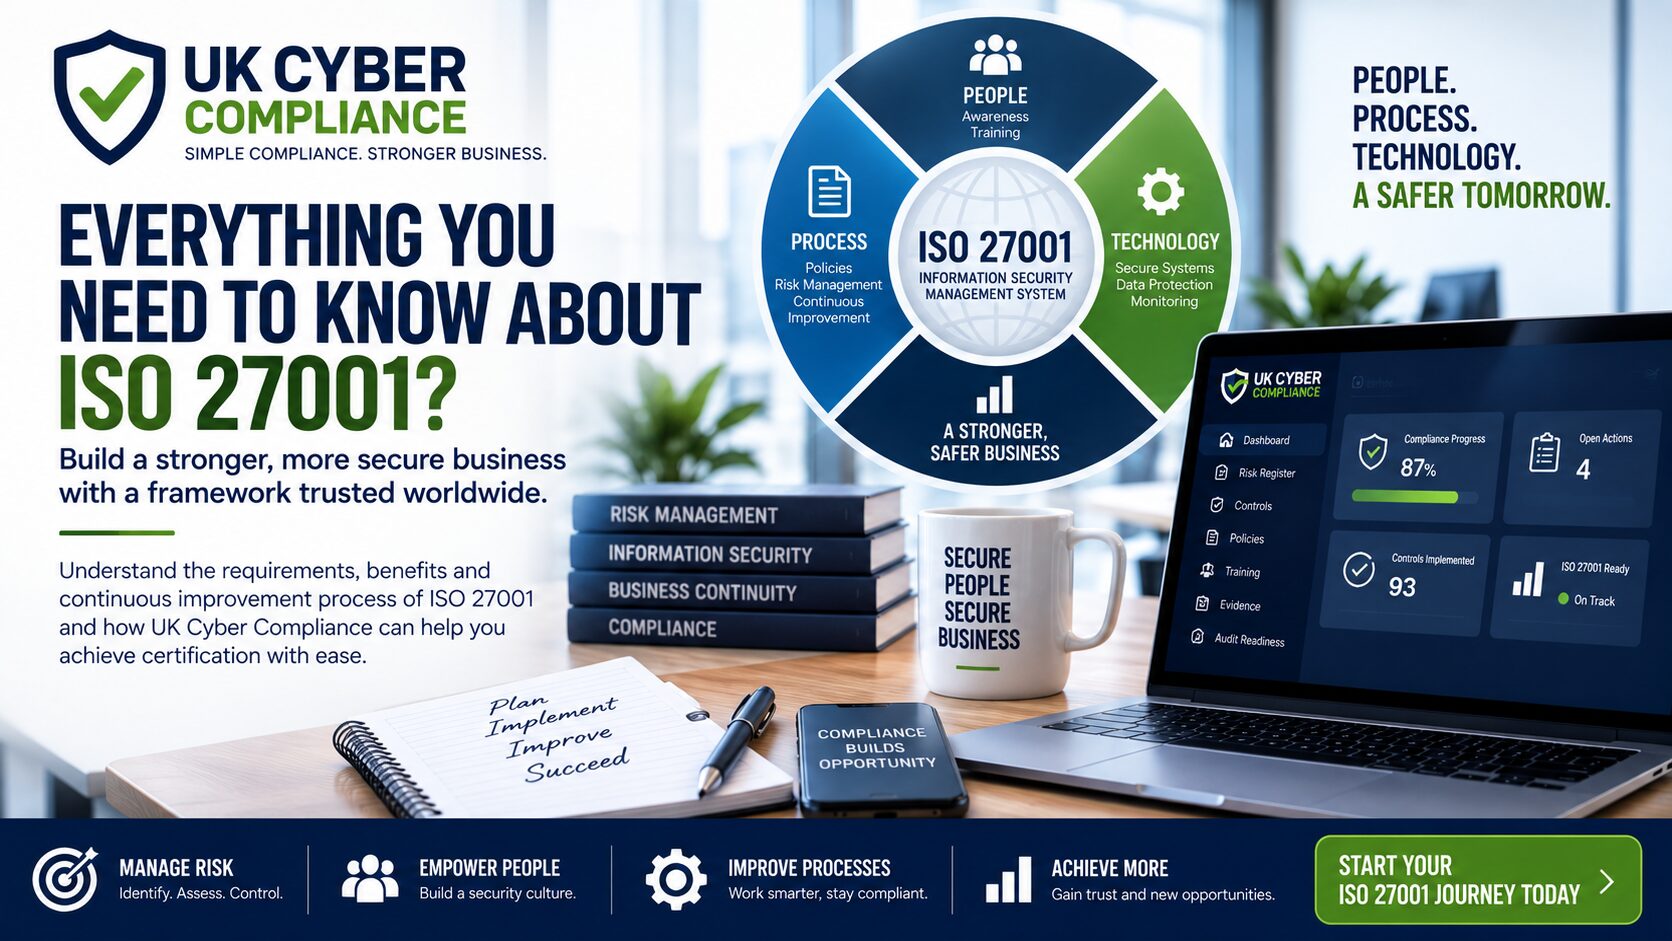
Everything you need to know about ISO 27001?
ISO 27001 is one of the world’s most recognised information security standards. It gives organisations a structured way to protect information, manage cyber risk, assign responsibility, measure security performance and continually improve how information security works across the business.
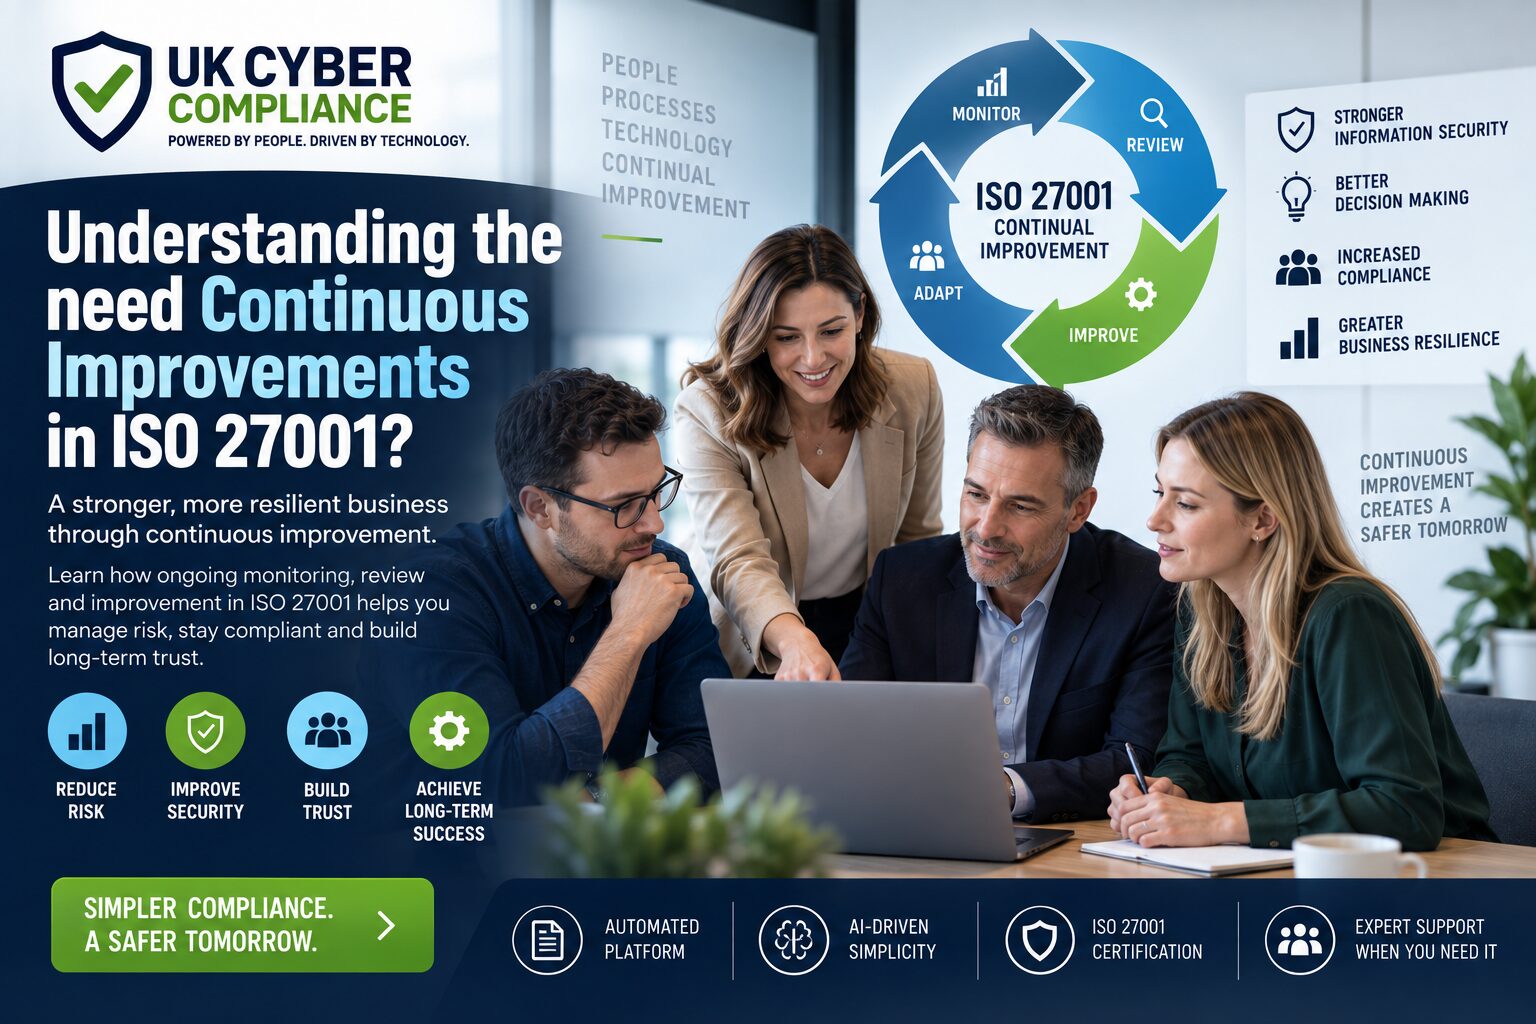
Understanding the need Continuous Improvements in ISO 27001?
Understanding the need Continuous Improvements in ISO 27001? starts with recognising that information security cannot remain static. Businesses change, technology develops, employees join and leave, suppliers change, new vulnerabilities appear and attackers adapt their methods. An Information Security Management System, commonly called an ISMS, needs to change with them.
Understanding the need to train the company in ISO 27001 for your business?
A company can deploy strong firewalls, multi-factor authentication, endpoint protection and security monitoring, but an employee can still expose sensitive information by responding to a convincing phishing email, sharing a document incorrectly, choosing the wrong recipient or failing to report suspicious activity.
Elevate Your Cybersecurity Standards
Join the forefront of cybersecurity excellence with UK Cyber Compliance. Our platform empowers businesses to achieve top-tier certifications like ISO 27001 and Cyber Essentials efficiently. Experience seamless compliance management with our AI-driven tools and expert support. Take the first step towards robust security and peace of mind.