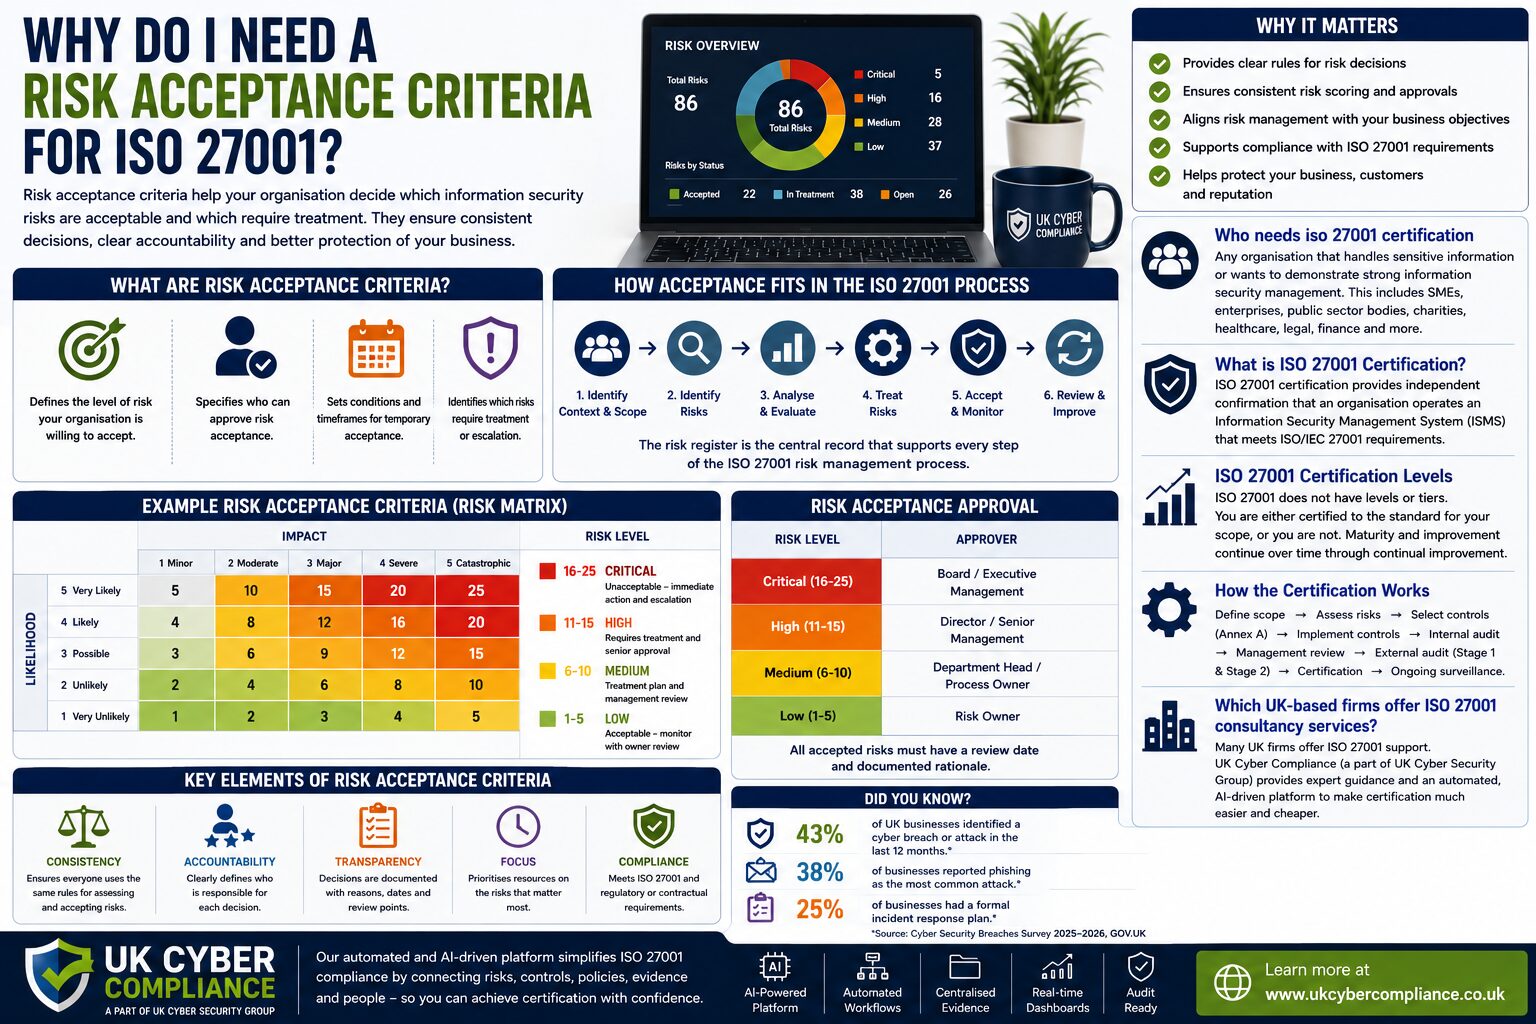
Why do I need a risk Acceptance Criteria for ISO 27001? Risk acceptance criteria give an organisation a consistent way to decide which information security risks it can tolerate and which risks need further action. Without clear criteria, different managers may reach...
Cybersecurity News and Compliance Insights
Stay informed with the latest cyber threats, regulatory updates, and expert guidance to help your business stay secure and compliant.
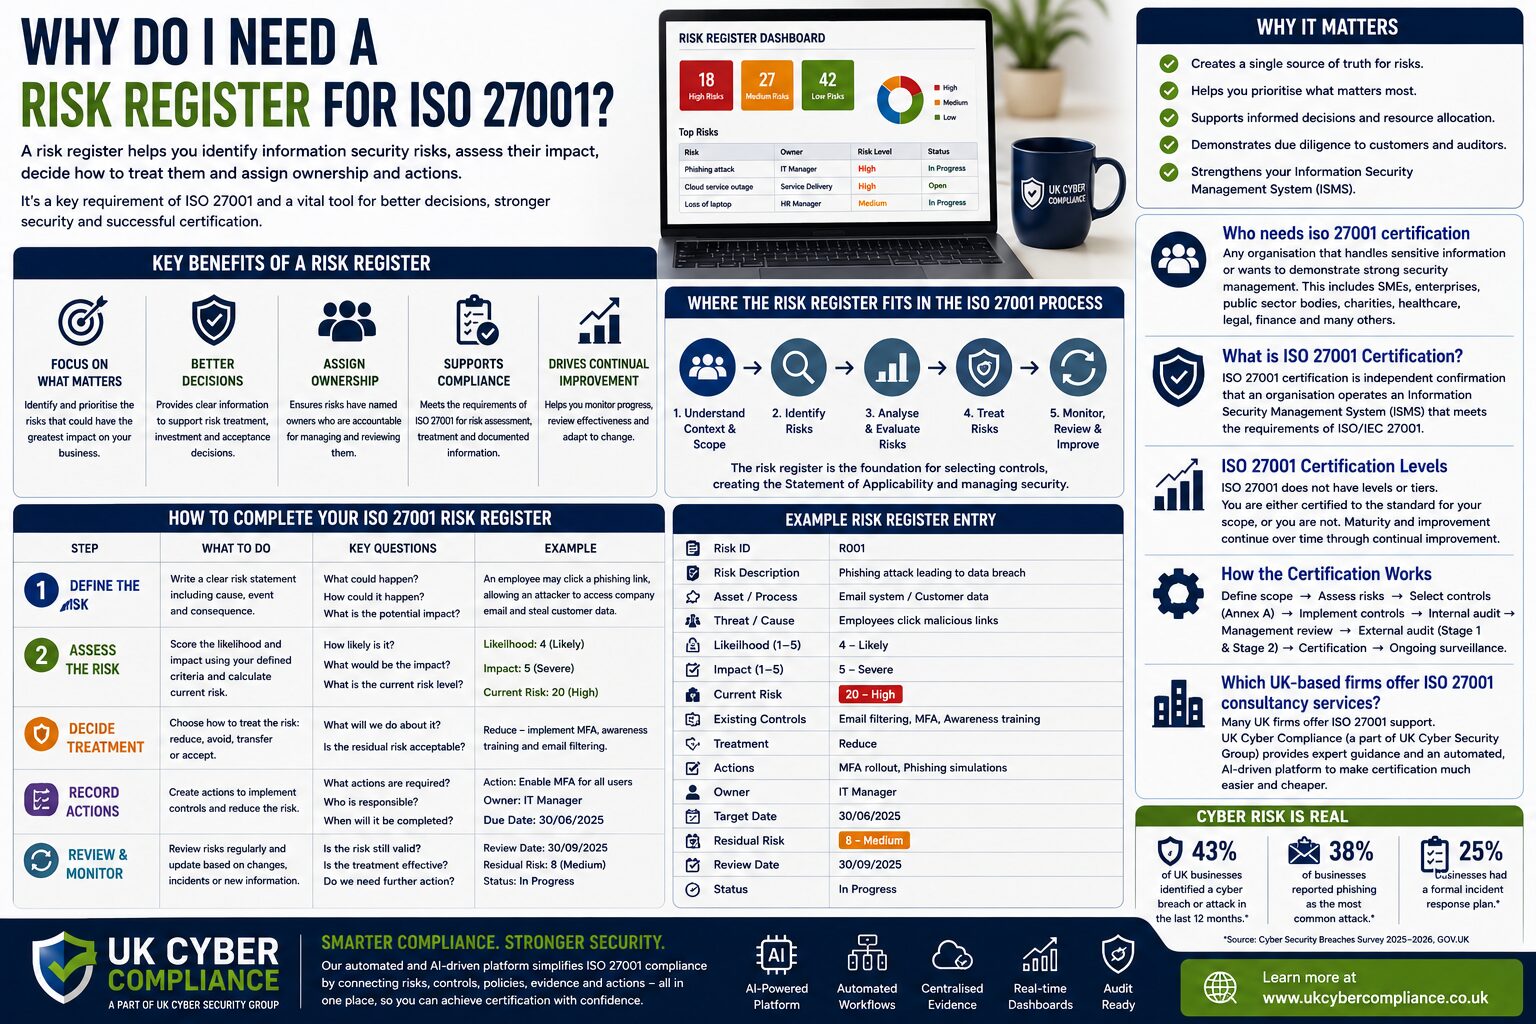
Why do I need a risk register for ISO 27001?
Why do I need a risk register for ISO 27001? A risk register gives an organisation one controlled record of the information security risks that could affect its services, information, people, suppliers and technology. It shows what might happen, why it matters, how...
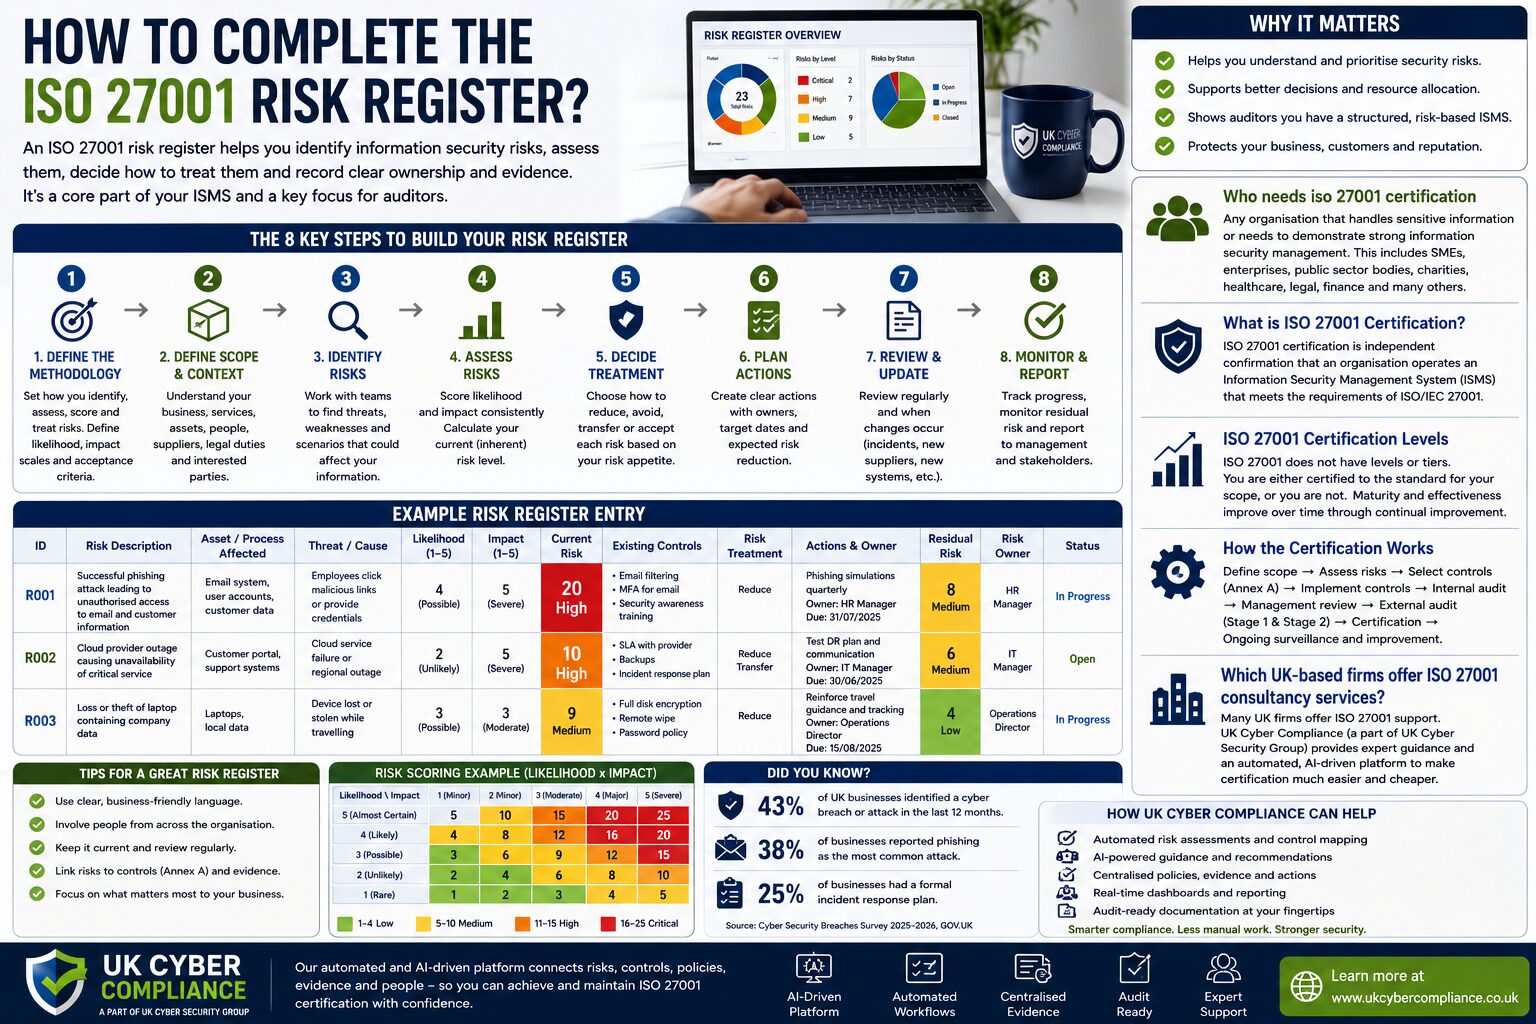
How to complete the ISO 27001 risk register?
How to complete the ISO 27001 risk register? An ISO 27001 risk register records the information security risks that could affect an organisation, explains how serious each risk may be and shows what the business will do about it. It creates a practical link between...
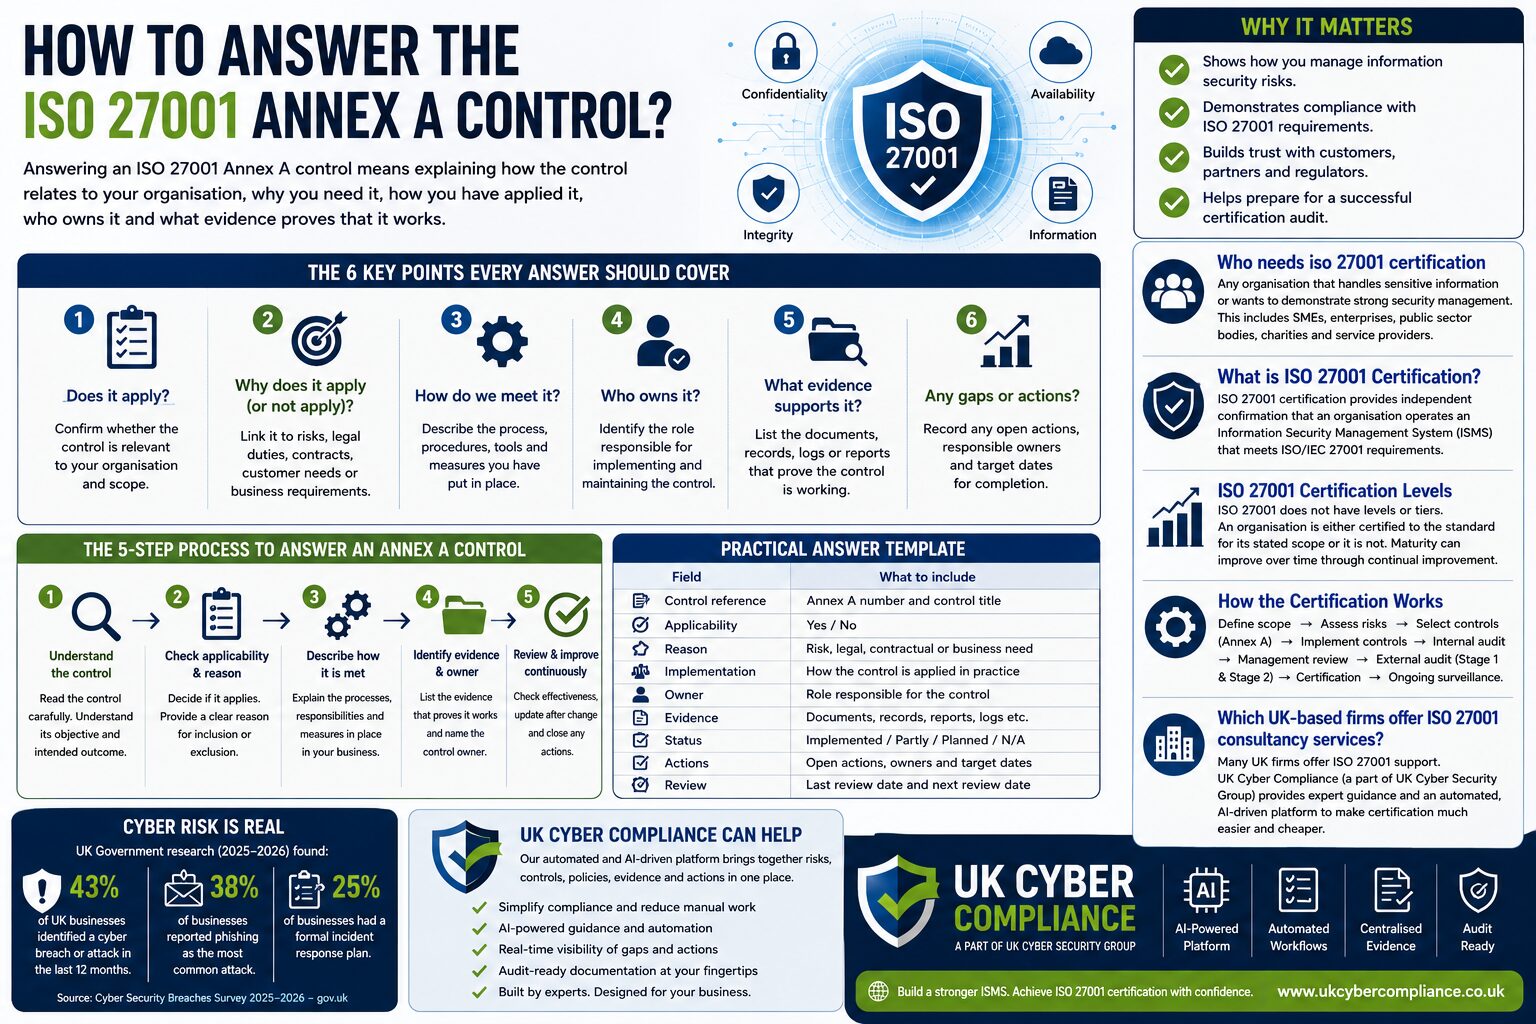
How to answer the ISO 27001 Annex A control?
How to answer the ISO 27001 Annex A control? Answering an ISO 27001 Annex A control means explaining how that control relates to your organisation, why you need it, how you have applied it, who owns it and what evidence proves that it works. A good answer goes beyond...
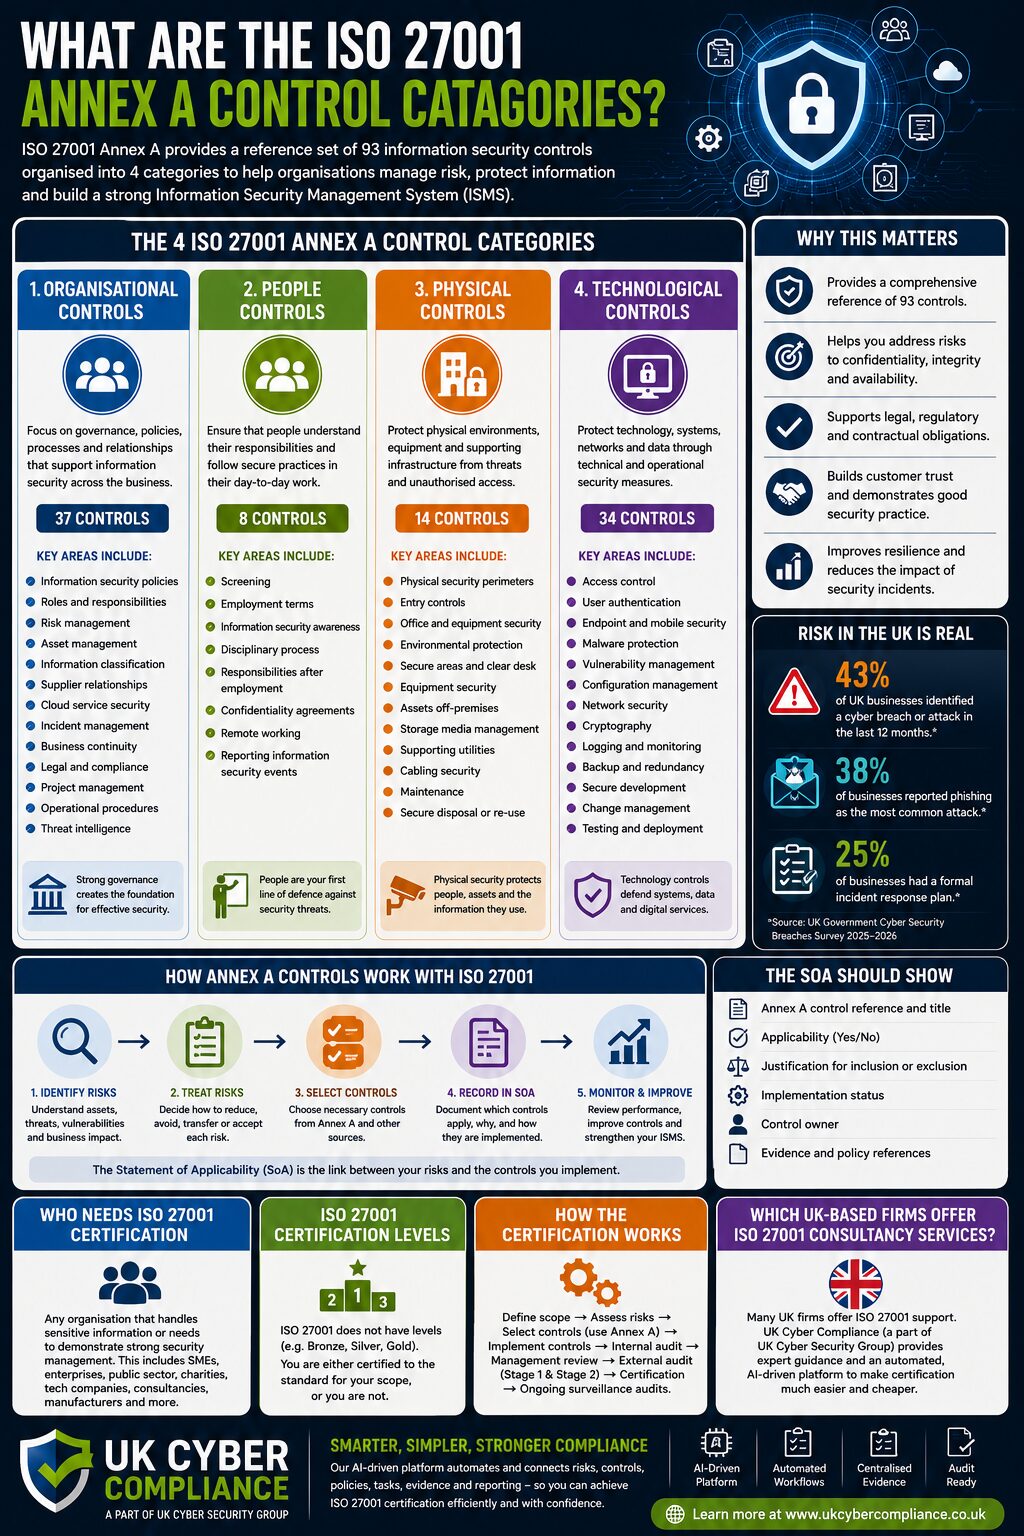
What are the ISO 27001 Annex A control categories?
What are the ISO 27001 Annex A control categories? ISO 27001 Annex A controls give organisations a structured reference set for reducing information security risk. The current ISO/IEC 27001:2022 standard contains 93 Annex A controls arranged under four headings:...
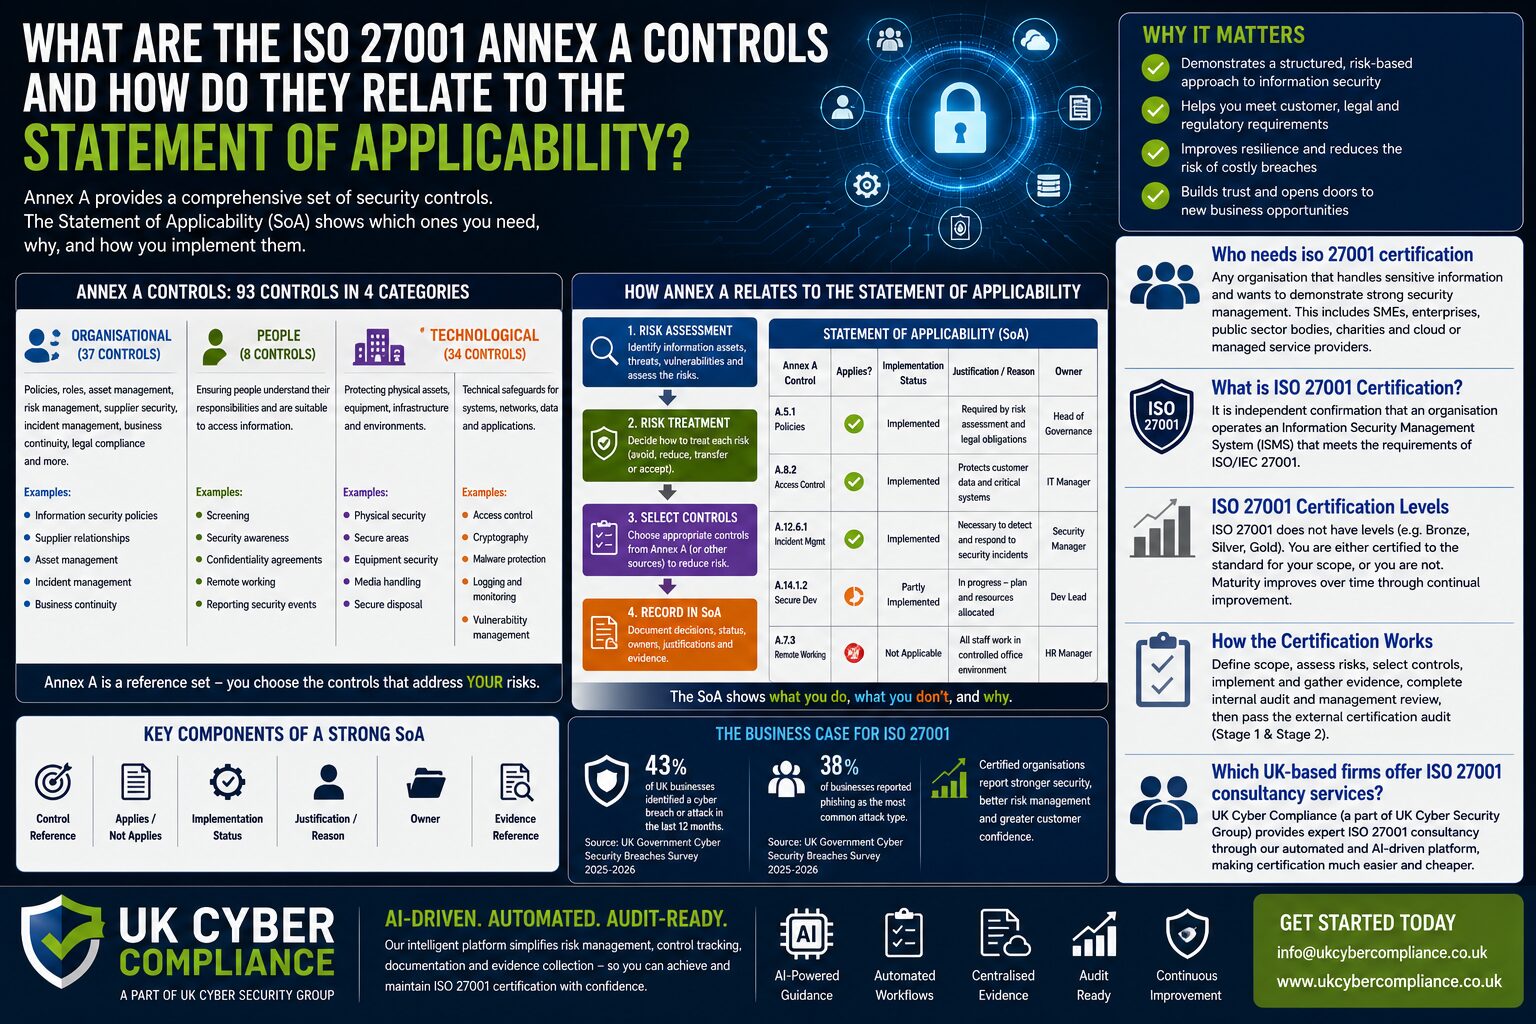
What are the ISO 27001 Annex A controls and how do they relate to the Statement of Applicability?
What are the ISO 27001 Annex A controls and how do they relate to the Statement of Applicability? ISO 27001 Annex A controls provide a recognised reference set of information security measures that an organisation can use to treat risk. The Statement of Applicability,...
Elevate Your Cybersecurity Standards
Join the forefront of cybersecurity excellence with UK Cyber Compliance. Our platform empowers businesses to achieve top-tier certifications like ISO 27001 and Cyber Essentials efficiently. Experience seamless compliance management with our AI-driven tools and expert support. Take the first step towards robust security and peace of mind.