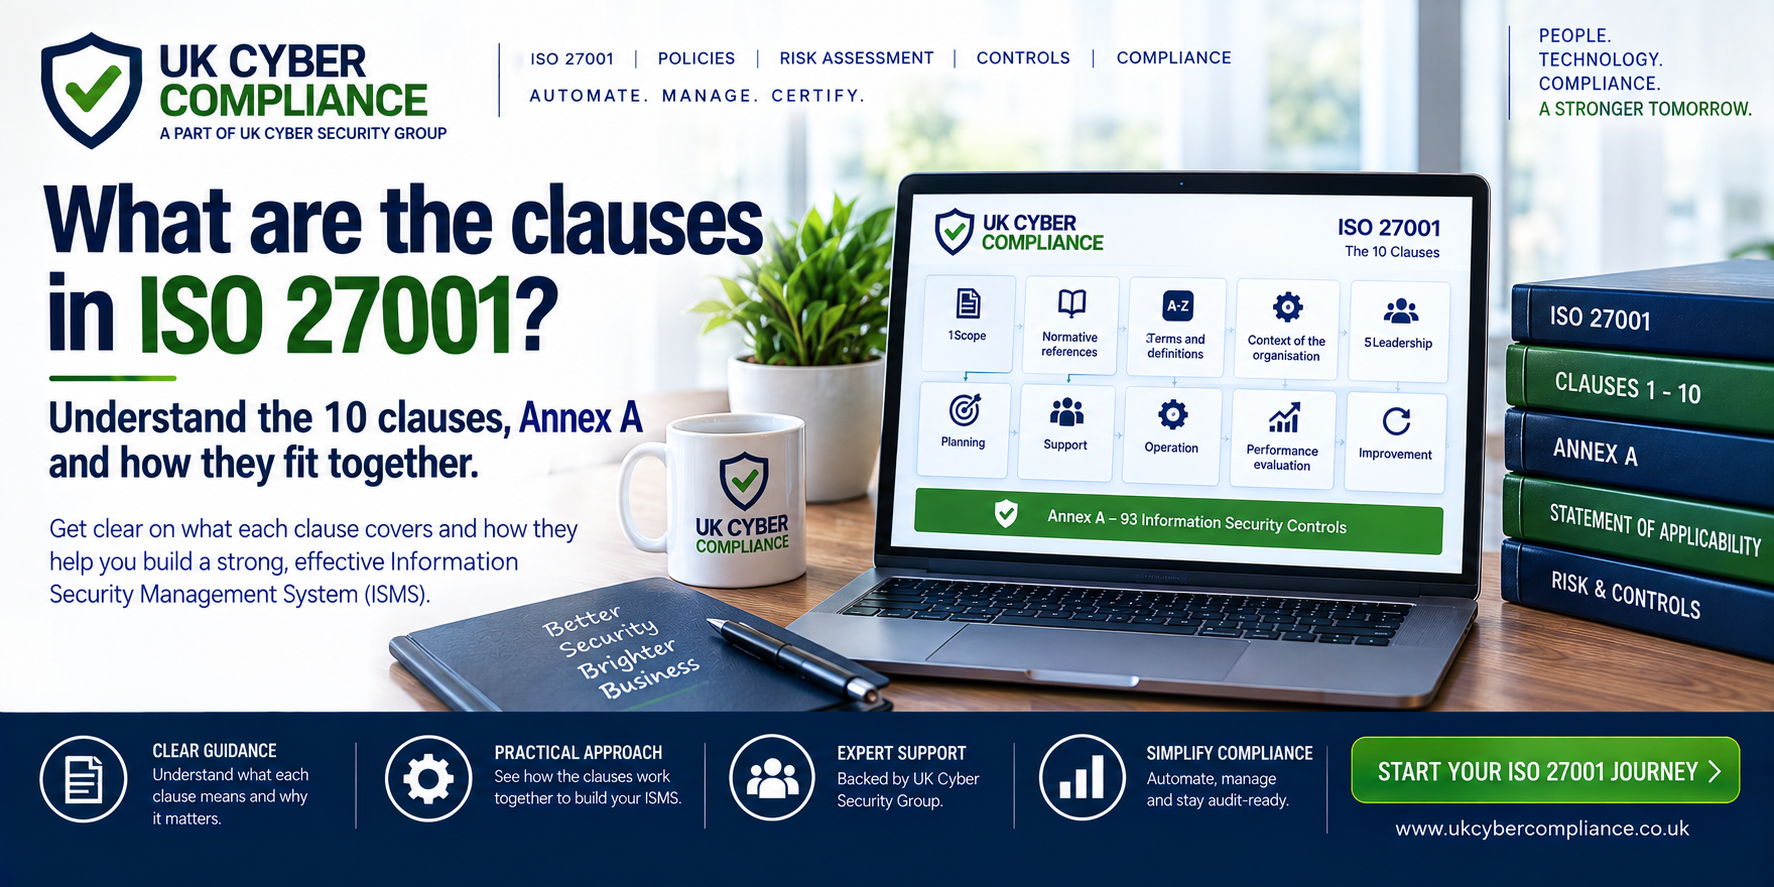
ISO/IEC 27001:2022 remains the current published edition of the international standard, supported by Amendment 1:2024 covering climate action changes. ISO describes ISO/IEC 27001 as the requirements standard for establishing, implementing, maintaining and continually improving an Information Security Management System.
Cybersecurity News and Compliance Insights
Stay informed with the latest cyber threats, regulatory updates, and expert guidance to help your business stay secure and compliant.
What is the easiest way of getting ISO 27001 certified?
Businesses often make ISO 27001 harder than it needs to be. They start by downloading large collections of policies, creating complicated spreadsheets and trying to interpret every Annex A control before they have even defined what their Information Security Management System needs to cover.
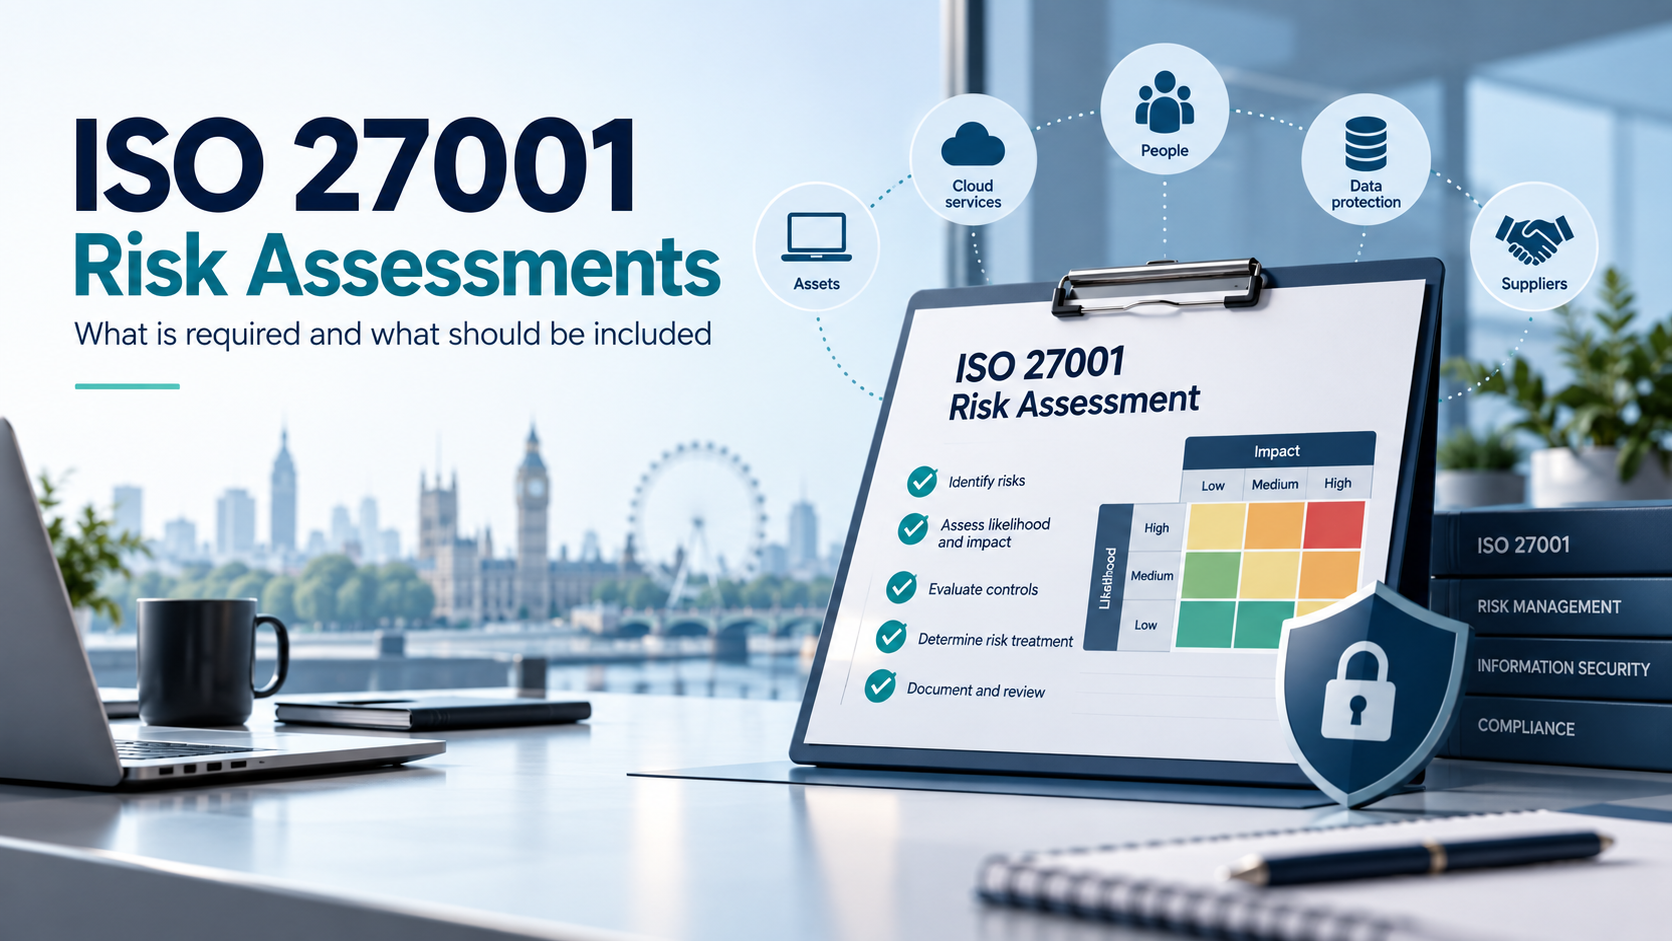
What risk assessments are required for ISO 27001, and what should be in them?
ISO/IEC 27001:2022 does not expect an organisation to choose security controls first and then find reasons to justify them. The organisation should understand its information security risks, evaluate those risks, decide which ones need treatment and then determine the controls required to reduce them to an acceptable level.
What processes are required for ISO27001 and what should be in them?
ISO 27001 is often described as a documentation standard, but that description misses an important point. Certification depends on processes that actually operate inside the business.
What policies are required for ISO27001 and what should be in them?
ISO 27001 certification involves policies, but one of the biggest mistakes businesses make is assuming they need dozens of separate policy documents simply because somebody has handed them a template pack.
What evidence will the ISO27001 auditor want to see?
Preparing for an ISO 27001 audit can feel daunting if you imagine the auditor arriving with a long checklist and expecting a perfect folder of documents. In practice, a good auditor wants something more useful: evidence that your Information Security Management System, or ISMS, operates as part of the business.
Elevate Your Cybersecurity Standards
Join the forefront of cybersecurity excellence with UK Cyber Compliance. Our platform empowers businesses to achieve top-tier certifications like ISO 27001 and Cyber Essentials efficiently. Experience seamless compliance management with our AI-driven tools and expert support. Take the first step towards robust security and peace of mind.