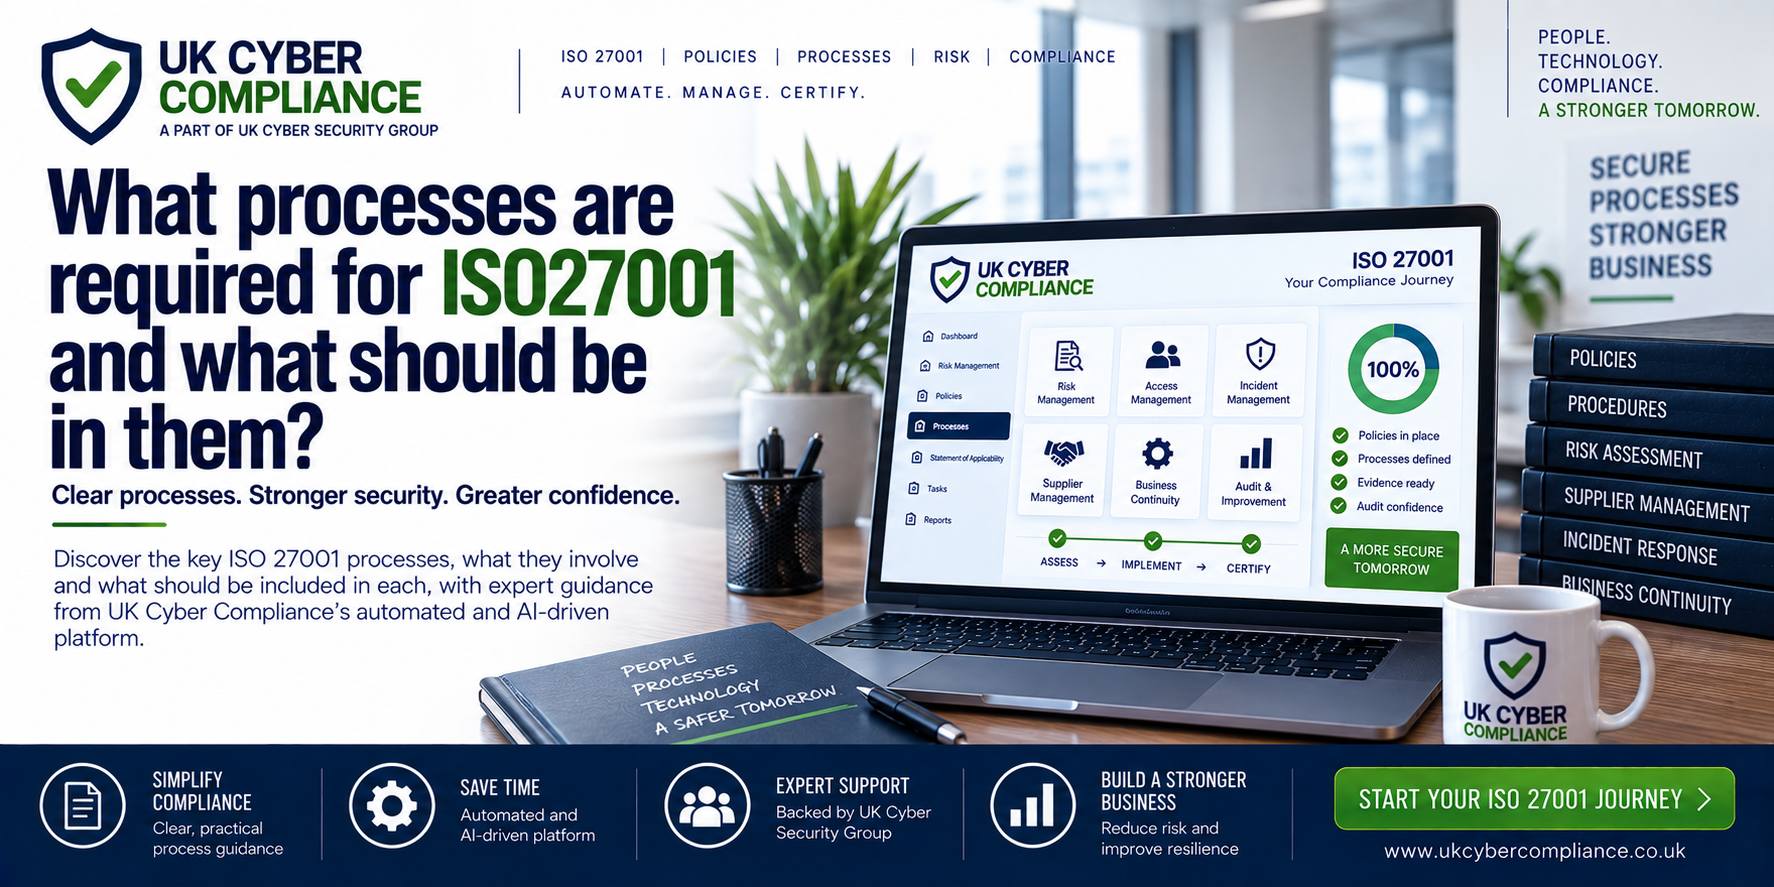
ISO 27001 is often described as a documentation standard, but that description misses an important point. Certification depends on processes that actually operate inside the business.
Cybersecurity News and Compliance Insights
Stay informed with the latest cyber threats, regulatory updates, and expert guidance to help your business stay secure and compliant.
What policies are required for ISO27001 and what should be in them?
ISO 27001 certification involves policies, but one of the biggest mistakes businesses make is assuming they need dozens of separate policy documents simply because somebody has handed them a template pack.
What evidence will the ISO27001 auditor want to see?
Preparing for an ISO 27001 audit can feel daunting if you imagine the auditor arriving with a long checklist and expecting a perfect folder of documents. In practice, a good auditor wants something more useful: evidence that your Information Security Management System, or ISMS, operates as part of the business.
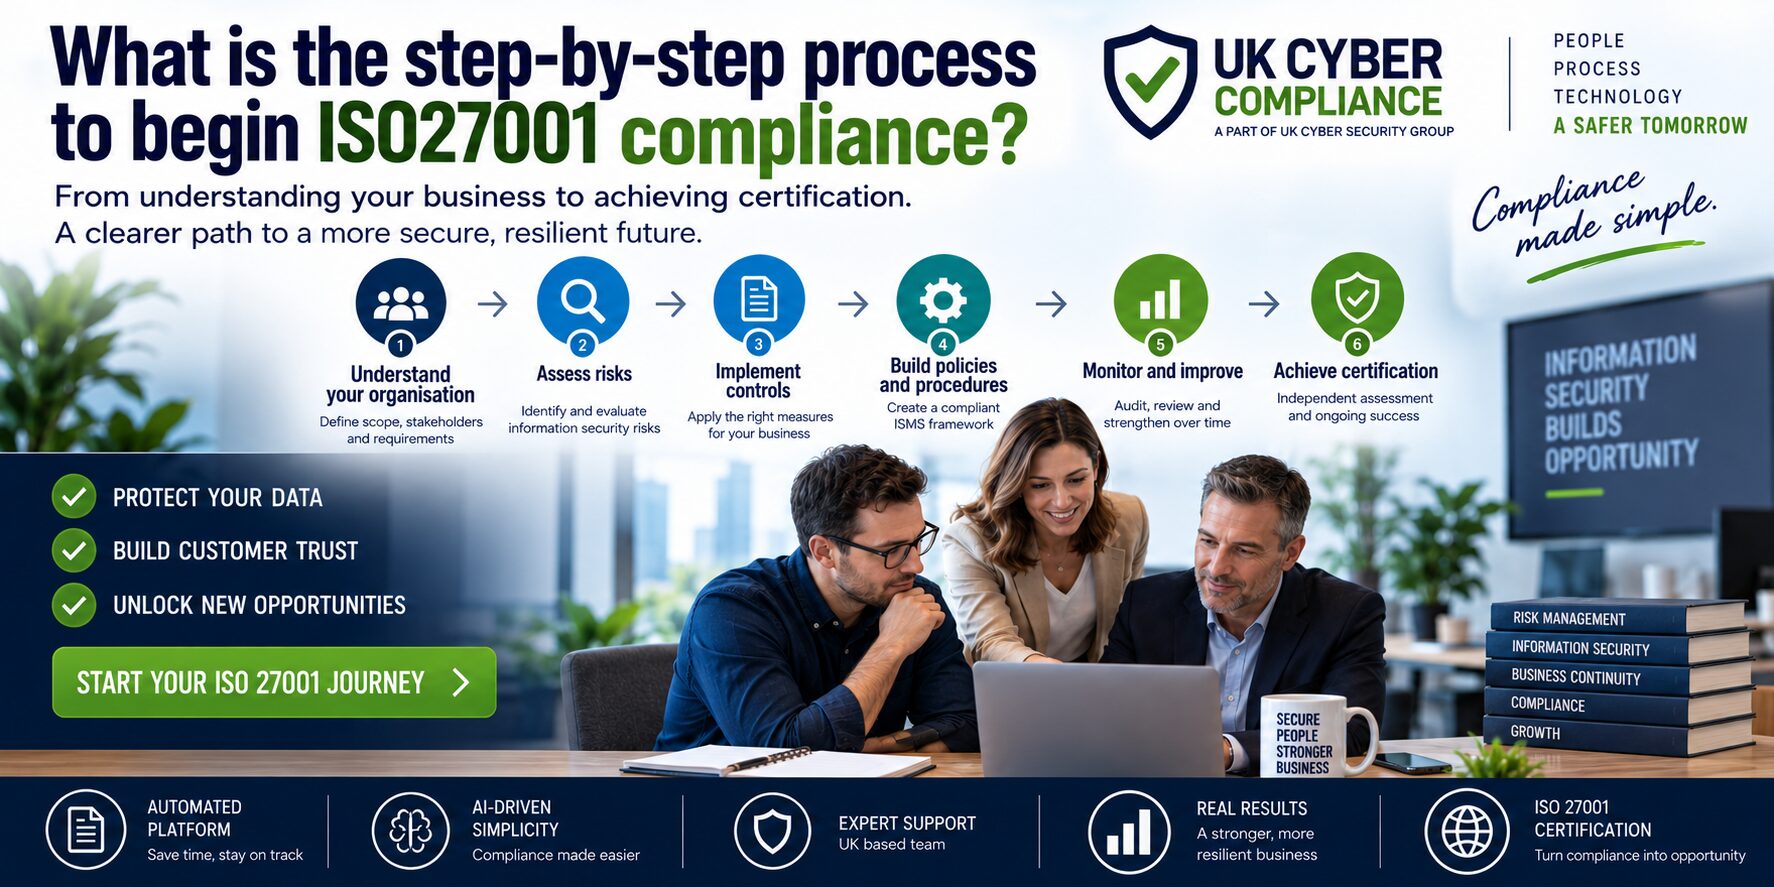
What is the step-by-step process to begin ISO27001 compliance?
The step-by-step process to begin ISO27001 compliance starts with understanding your organisation rather than immediately writing policies or working through security controls.
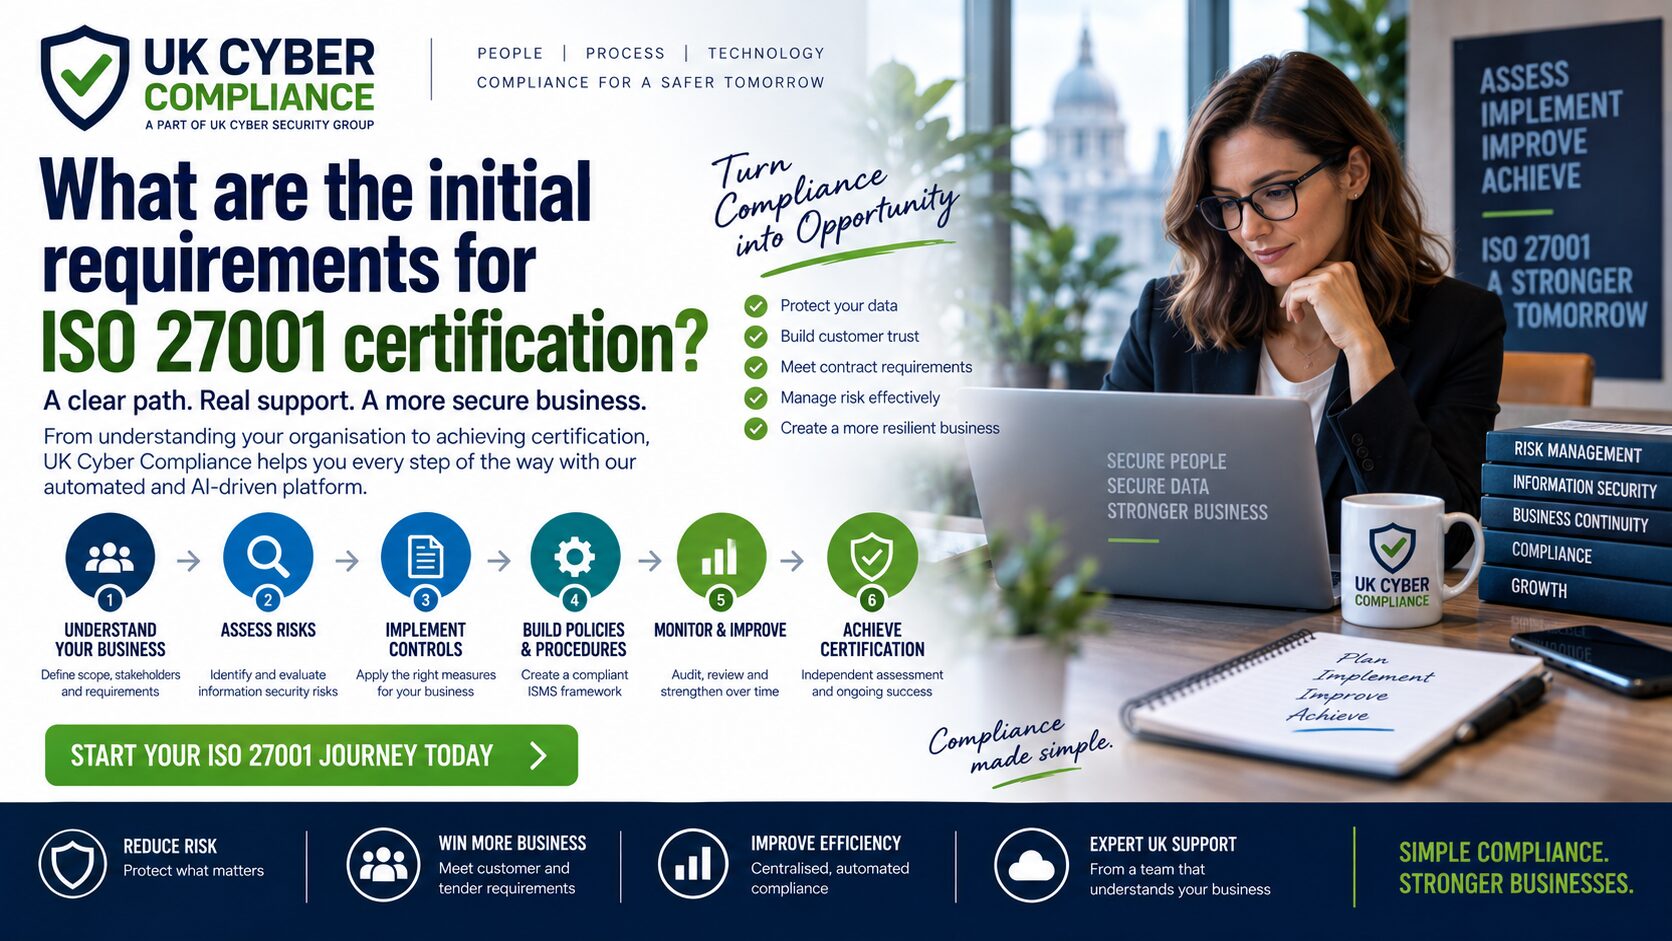
What are the initial requirements for ISO 27001 certification?
The initial requirements for ISO 27001 certification start long before an external auditor arrives. A business first needs to understand why it wants certification, what part of the organisation the Information Security Management System will cover, who will take responsibility for it, what information needs protection and which security risks matter most.
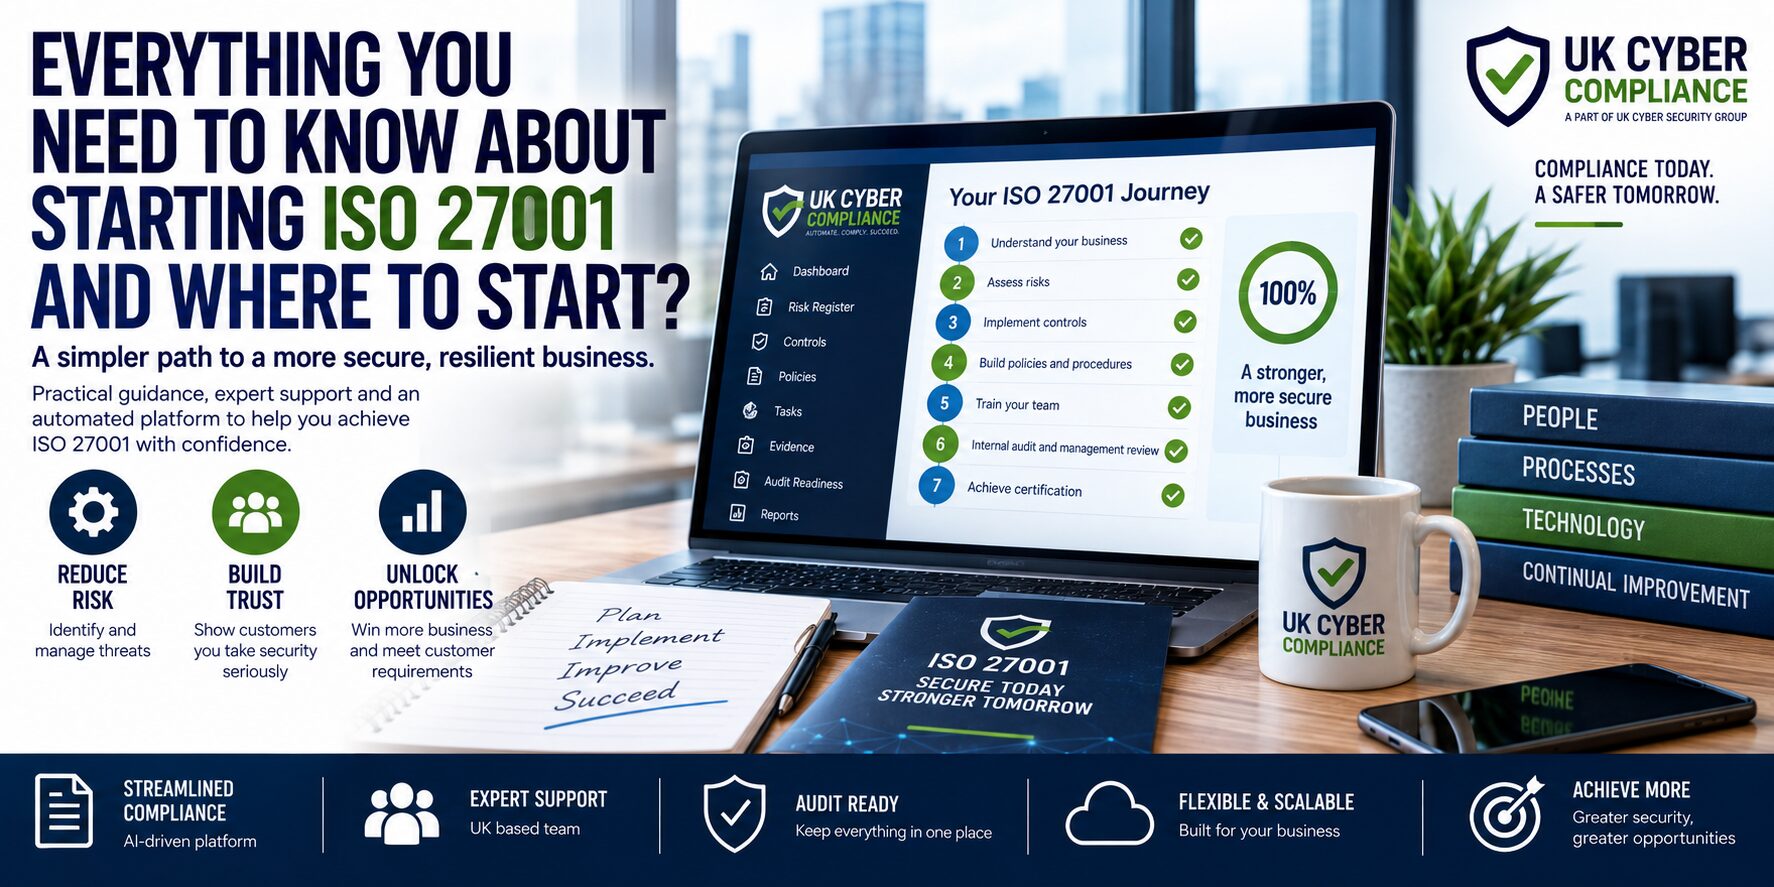
Everything you need to know about starting ISO 27001 and where to start?
Starting ISO 27001 can look complicated when you first see the standard. There are risks to assess, controls to consider, policies to prepare, responsibilities to assign, audits to complete and evidence to gather.
Elevate Your Cybersecurity Standards
Join the forefront of cybersecurity excellence with UK Cyber Compliance. Our platform empowers businesses to achieve top-tier certifications like ISO 27001 and Cyber Essentials efficiently. Experience seamless compliance management with our AI-driven tools and expert support. Take the first step towards robust security and peace of mind.